Phishing detection & brand protection for Kuwait
KWTCyberWatch watches Certificate Transparency logs the moment certificates are issued, hunts typosquats of Kuwaiti banks, telecoms and government services, and turns every look-alike into a triaged alert. No third-party feed. Nothing leaves your browser.
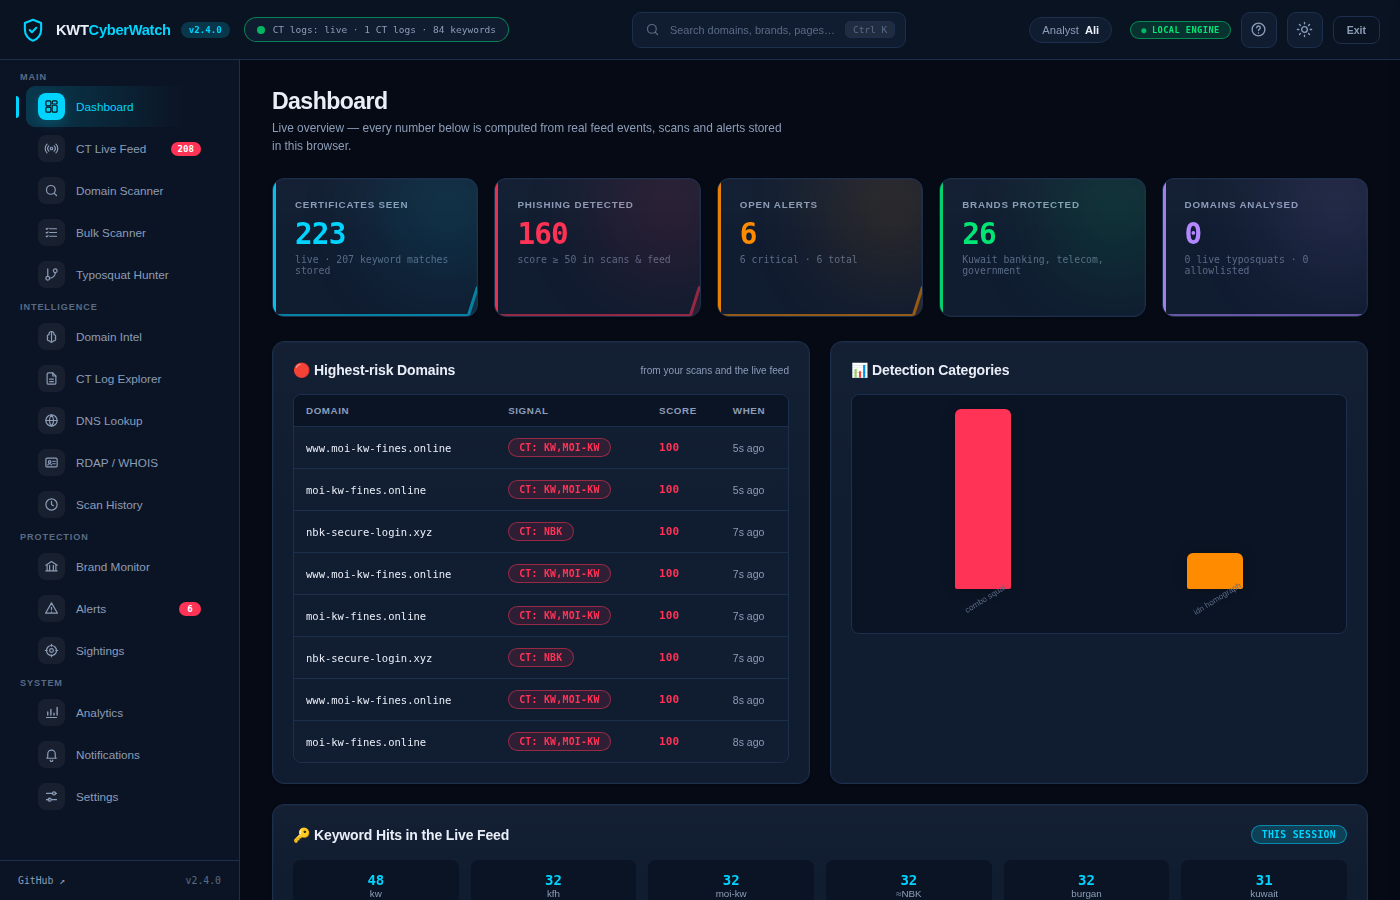
Built for analysts, not demos
Every number in the console comes from real Certificate Transparency entries, real DNS answers and real registration data. The full detection engine is ported to JavaScript and parity-tested against the Python backend.
Direct CT log tailing
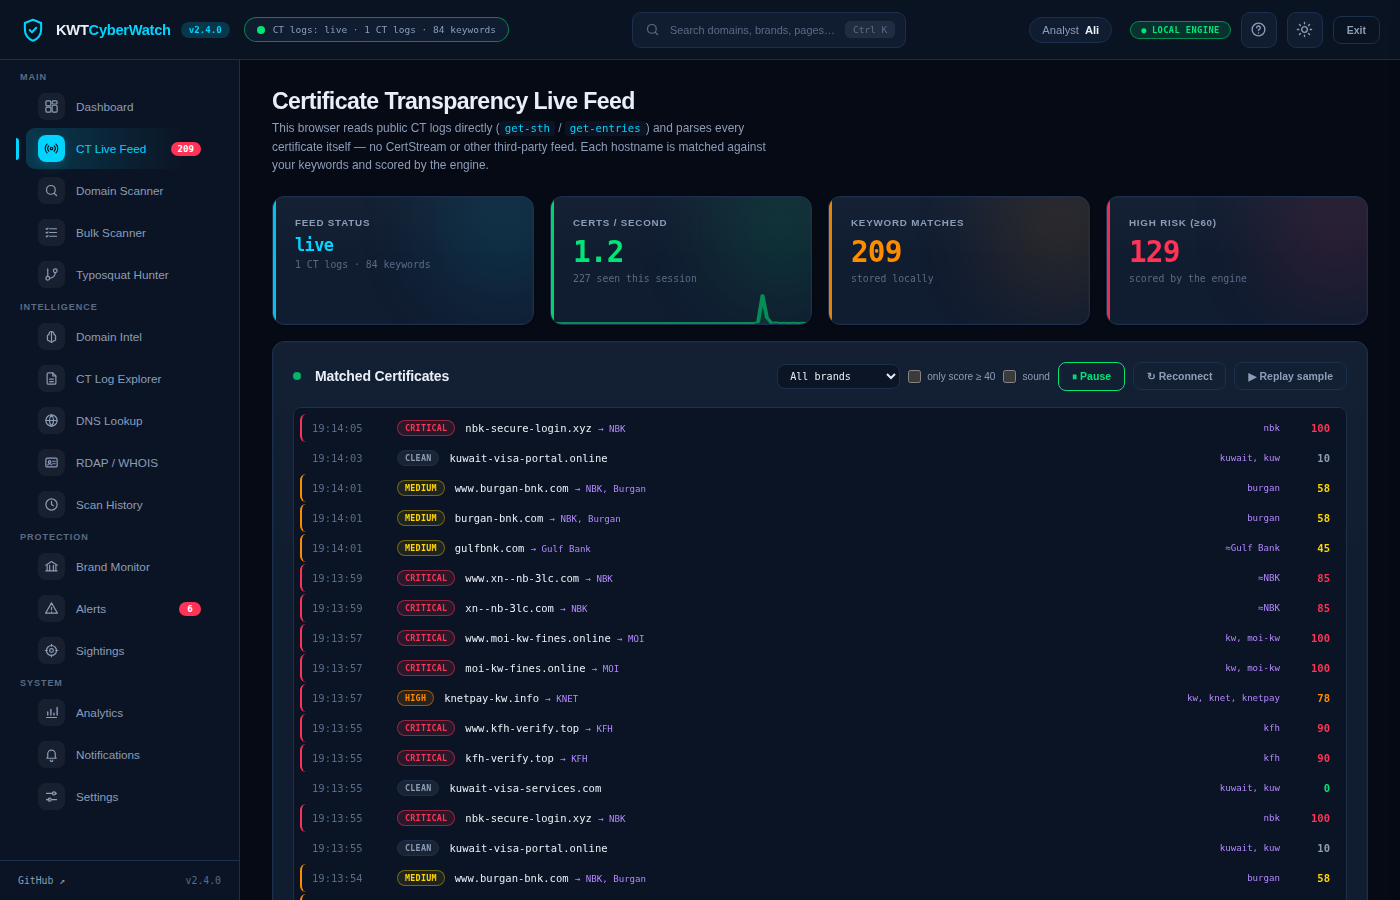
Reads RFC 6962 and Static CT API logs itself, parses every DER certificate with a built-in reader and scores each hostname as it is logged.
Typosquat Hunter & Watchtower
Generates typos, homoglyphs, leet, combo-squats and TLD swaps for any brand, resolves them over DNS-over-HTTPS and sweeps protected brands on a schedule.
IDN & Arabic aware engine
Detects Cyrillic homoglyphs such as nbк.com, mixed scripts and Arabic lures like بيتك-تحديث, with a character inspector and a look-alike diff for every verdict.
Alert lifecycle
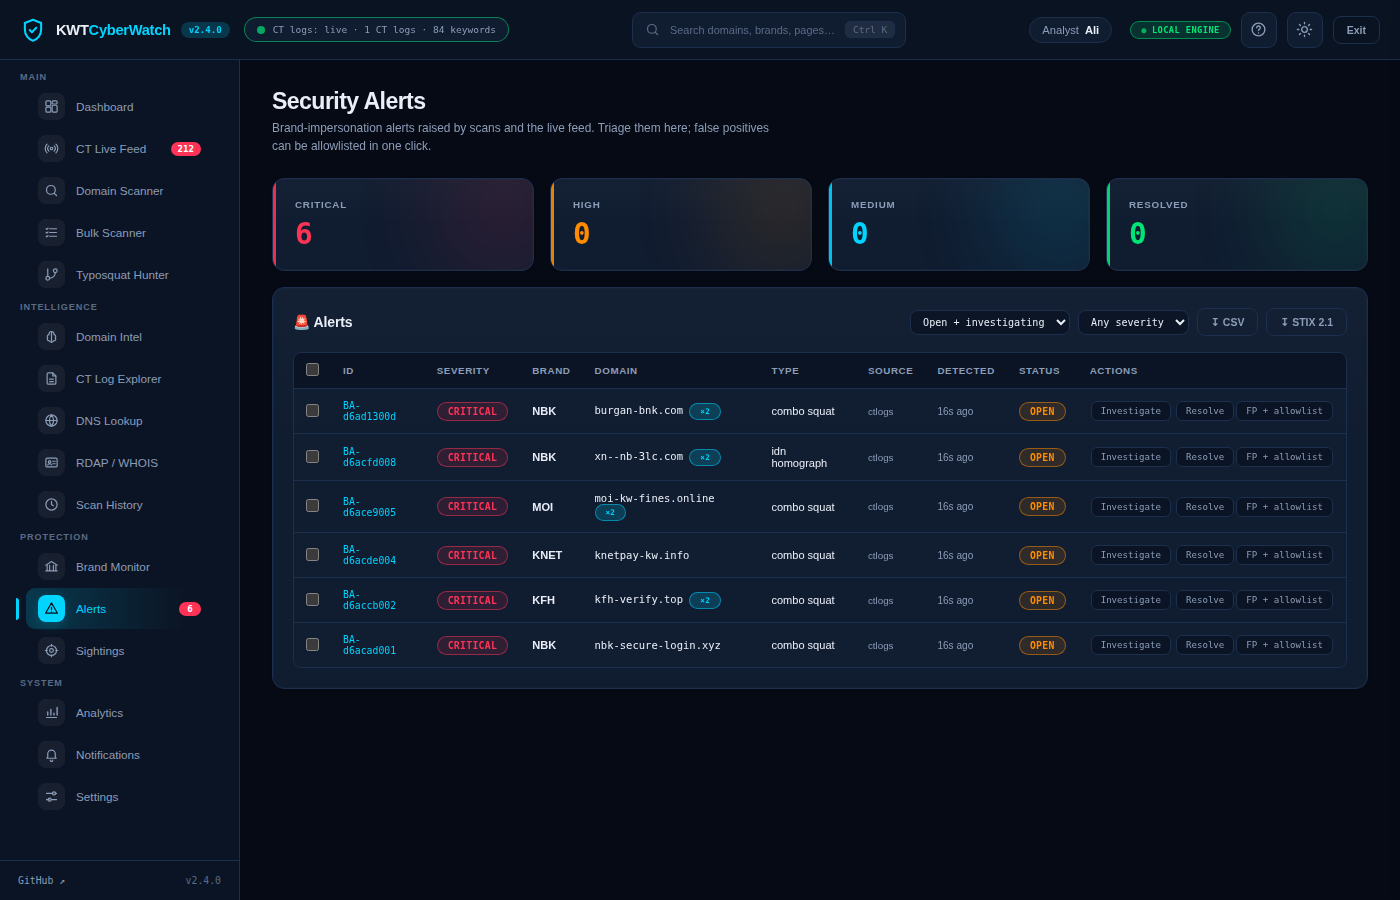
Open → investigating → resolved / false positive, notes, assignee, timeline, bulk triage, one-click allowlisting, consolidated per domain.
Custom detection rules
Regular-expression rules with severity, tested inline and applied to every certificate and scan. Deep match runs the brand engine on every hostname, keyword or not.
Real enrichment
DNS-over-HTTPS (Google, Cloudflare fallback), crt.sh certificate history, RDAP registration age and URLhaus reputation, fetched directly from the browser.
Reports & exports
STIX 2.1 bundles, CSV, per-alert and weekly HTML reports, IOC copy, and a JSON backup of the whole workspace.
Installable console
Command palette (Ctrl+K), deep links, keyboard shortcuts, light and dark themes, and a service worker so the console opens offline as a PWA.
How it works
Three sources feed one engine. Everything is computed locally, so the console behaves the same on GitHub Pages and on an air-gapped analyst laptop.
Discover
Certificates arrive from the CT logs you tail directly; look-alikes come from the Typosquat Hunter and the scheduled Watchtower sweep; anything else you paste into the scanner or the bulk scanner.
Detect
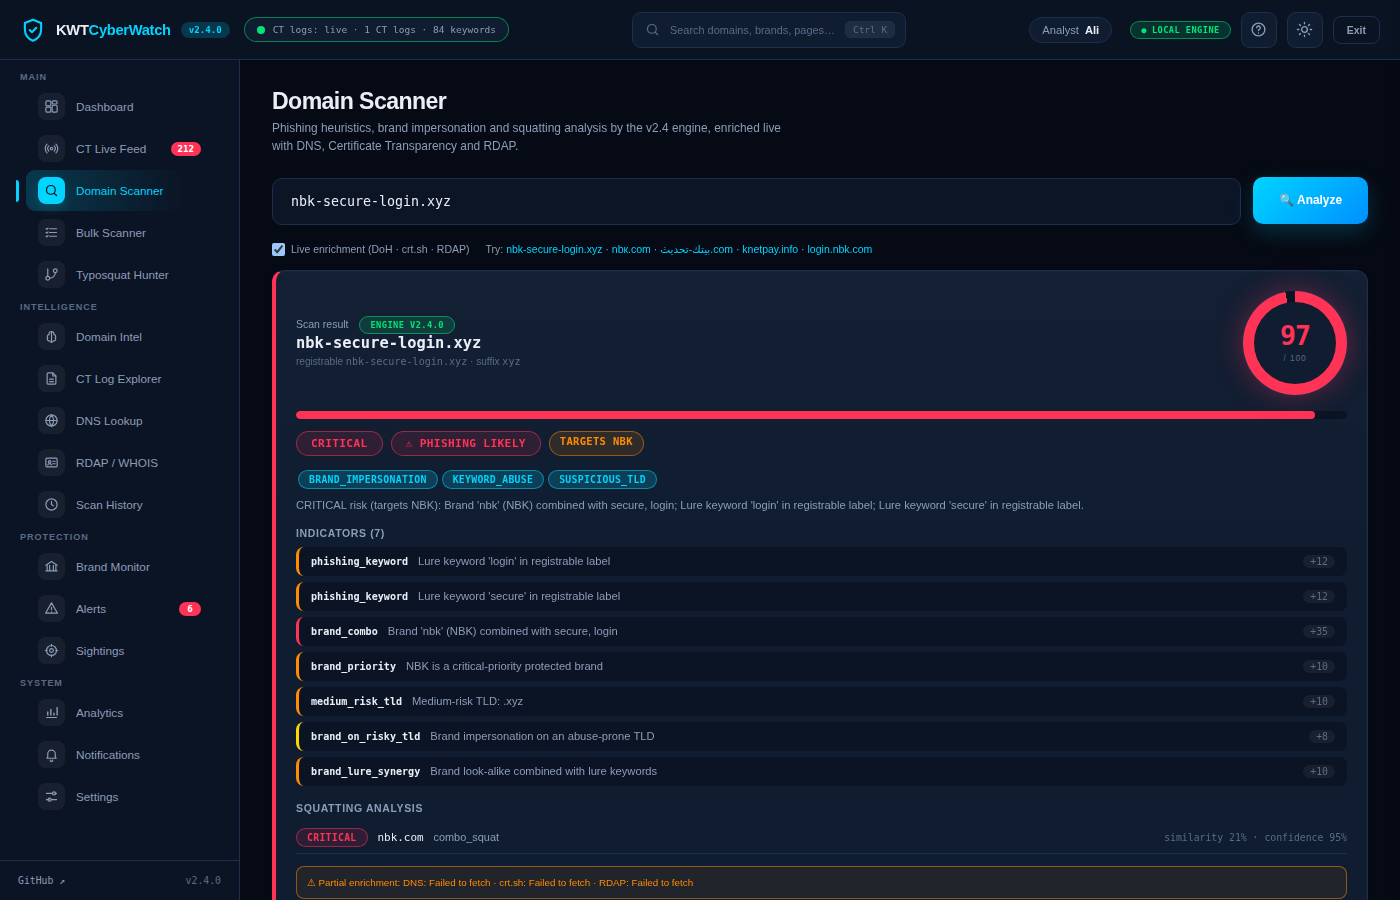
The engine parses the registrable domain, folds confusables and leetspeak, checks 26 Kuwaiti brand profiles and 84 keywords, scores lures, risky TLDs, entropy and hosting platforms, then applies your custom rules.
Triage
Alerts are enriched with DNS and registration age, consolidated per domain, and worked in a drawer with evidence, diff, notes and timeline. Export STIX or a report when you hand off.
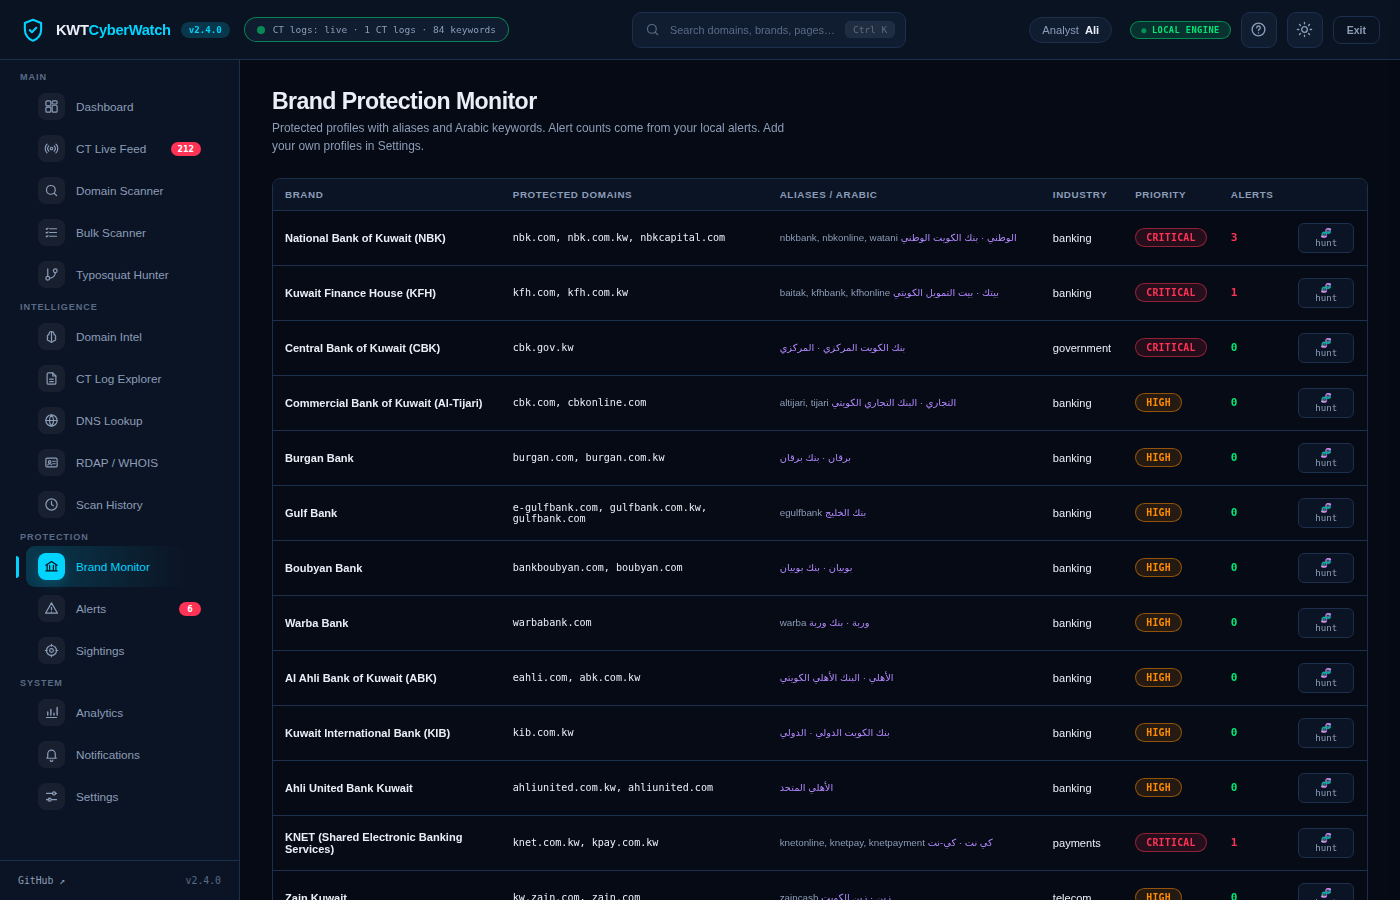
Inside the console
Screens captured from the console while tailing a live Certificate Transparency log.
Self-host the backend optional
The browser console needs no server. For 24/7 monitoring, notifications to Slack, Teams, Telegram, e-mail or Syslog/CEF, and a REST API with OpenAPI docs, run the Python backend.
# clone and install
git clone https://github.com/SiteQ8/KWTCyberWatch.git
cd KWTCyberWatch && pip install -r requirements.txt

# scan a domain
python main.py scan nbk-secure-login.xyz

# tail CT logs directly (no third party)
python main.py monitor

# proactive typosquat watcher + API + dashboard
python main.py watch-squats
python main.py api            # http://localhost:5000

# or everything at once
docker compose up -d
- Engine
- Python 3.10+, dependency-free X.509 parser, SQLite with migrations
- CT sources
- RFC 6962 and Static CT API logs discovered from Google's log list; legacy CertStream WebSocket optional
- Intel
- OpenPhish and URLhaus out of the box; VirusTotal, URLScan, PhishTank and Google Safe Browsing with a key
- Outputs
- STIX 2.1, CSV, Markdown/JSON reports, Prometheus metrics, Syslog/CEF
- API
- Signed bearer tokens, roles, rate limiting, OpenAPI at
/api/v1/docs - License
- MIT · built by Ali AlEnezi (SiteQ8)
Important notice
KWTCyberWatch produces automated heuristic findings from public data. A flagged domain is a candidate for review, not an accusation, and legitimate services will appear among the results. Verify independently before blocking, reporting or attributing. Brand names are used for identification only and remain the property of their owners. The software, site and published feed are provided as is, without warranty or liability. The console stores data only in your browser; this site sets no cookies and runs no analytics. Read the full disclaimer and terms of use.